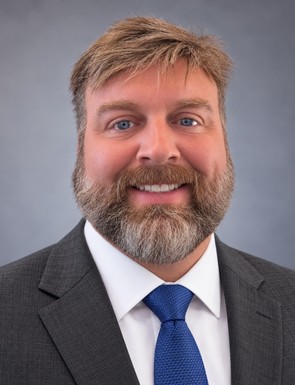
Tom Greer, CISSP
Tom leads SolluCIO's cybersecurity practice and serves as a fractional CISO for clients who need executive-level security leadership without the executive-level payroll. He has spent more than 25 years in IT and information security, including in-house roles as Chief Information Security Officer and Director of Information Security, and he brings that operator's perspective to every engagement: security programs that leadership teams can actually run, auditors can actually verify, and customers can actually trust.
His work comes down to keeping clients secure and compliant, in that order. Keeping you secure — Tom builds security programs from the ground up: identifying the risks that matter to your business, hardening the environment with zero-trust architectures and layered defenses, and putting the people, processes, and monitoring in place so threats are caught early and handled without drama. Keeping you compliant — with the fundamentals in place, compliance becomes a byproduct rather than a scramble. Tom has built and run programs against SOC 2, ISO 27001, NIST, and HIPAA, with a bias toward evidence that holds up under audit rather than paperwork that sits in a drawer. Clearing the path for new products — he has led the security and compliance workstreams for medical-device launches through FDA and HIPAA requirements, and secured platforms in fintech and Web3 where the threat model changes monthly.
Tom works with growing companies across healthcare, medical devices, financial services, and technology — typically as an embedded member of the leadership team rather than an outside auditor.