CYBERSECURITY & AI GOVERNANCE

Cybersecurity that
enables growth.

Executive leadership, practical cybersecurity, and responsible AI governance. Reduce risk, strengthen readiness, and move your business forward.

Cybersecurity. Built on trust.Our approach to protecting what matters · 90-second overview

Built for organizations where trust matters.

  • Healthcare
  • Medical devices
  • Fintech
  • Regulated businesses

WHAT WE DO

Seven capabilities.
One accountable partner.

Start with your most urgent need.
Add expertise as your priorities evolve.

01

Fractional &
interim CISO

Get executive direction and clear accountability without a full-time hire.

What’s included
  • Executive advisory and board reporting
  • Security strategy and investment priorities
  • Interim leadership and team coaching
02

AI governance &
ISO/IEC 42001

Adopt AI responsibly with clear accountability, risk oversight, and an AI management system.

What’s included
  • ISO/IEC 42001 readiness assessment and AI management system implementation support
  • AI inventory, use cases, supplier oversight, and risk and impact assessments
  • Policies, accountable roles, decision processes, and human oversight
  • Evidence, monitoring, review, and continual improvement
About the ISO/IEC 42001 standard ↗Connect data & governance ↗
03

Risk, readiness
& compliance

Turn competing requirements into a prioritized, defensible readiness plan.

What’s included
  • Risk and maturity assessments
  • HIPAA, SOC 2, NIST CSF, ISO 27001 and HITRUST readiness
  • Gap analysis, remediation planning and audit preparation
04

Specialized
cybersecurity talent

Fill critical skills gaps and add the capacity your team needs to deliver.

What’s included
  • Specialist staff augmentation
  • Executive search and placement
  • Talent assessment and leadership development
05

Governance &
program development

Connect policies, controls, and people into a program that can scale.

What’s included
  • Policies and operational playbooks
  • Enterprise and vendor risk management
  • Control ownership, evidence and reporting cadence
  • M&A due diligence and integration planning
06

FDA &
product security

Bring cybersecurity evidence and secure development into product readiness.

What’s included
  • 510(k) cybersecurity readiness and submission support
  • Threat modeling and product risk documentation
  • Secure development lifecycle evidence
Explore FDA readiness advisory ↗
07

Managed
security services

Support day-to-day protection with monitoring, response, and operational expertise.

What’s included
  • SOC monitoring and managed detection and response
  • Vulnerability and patch management
  • Identity and access management
  • Security technology implementation and tuning

CLIENT SUCCESS SPOTLIGHT

From product risk
to regulatory
readiness.

Remote patient monitoring
Healthcare & medical devices

Explore FDA readiness advisory
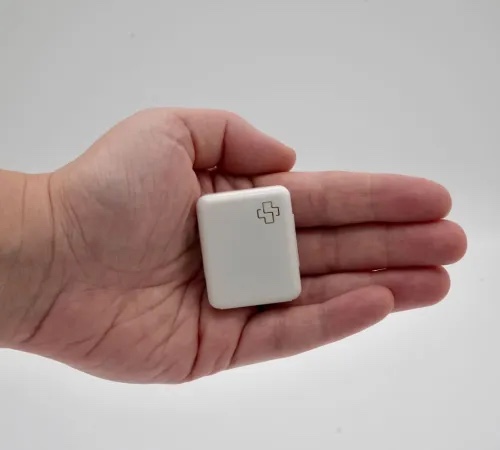
The Perin Health Patch resting in the palm of a hand
Perin Health PatchPhoto: Perin Health ↗
CLIENT OUTCOME

FDA 510(k) cleared.

Perin Health System (PHD80060-2)

K252984 January 22, 2026

View the FDA clearance

The challenge

Align product cybersecurity and regulatory evidence while strengthening the organization’s broader security program.

Our contribution

Cybersecurity workstream led by Sollucio Partners, including threat modeling, product security risk, secure development lifecycle evidence, documentation, and regulatory submission support.

The engagement also strengthened governance, control evidence, and compliance readiness across the security program.

WHY SOLLUCIO

Senior expertise.
Practical execution.

You need a partner who can advise the board, work alongside your team, and stay accountable.

Illustration of a senior advisor and business leaders reviewing a practical program roadmap
Senior-led

Experienced practitioners stay engaged from strategy through execution.

Independent

Advice shaped by your priorities, with no software quota or product agenda.

Practical

Clear priorities and roadmaps designed to be implemented.

Business-aligned

Cyber risk translated into decisions your leadership team can act on.

HOW WE WORK

From pressure to progress.

A clear path from understanding the risk to running a stronger program.

  1. Assess.

    Understand your business, obligations, maturity, and near-term exposure.

  2. Prioritize.

    Build a risk-based roadmap with clear owners and investment priorities.

  3. Build.

    Put governance, controls, evidence, and repeatable processes into practice.

  4. Lead.

    Maintain executive oversight, useful reporting, and ongoing improvement.

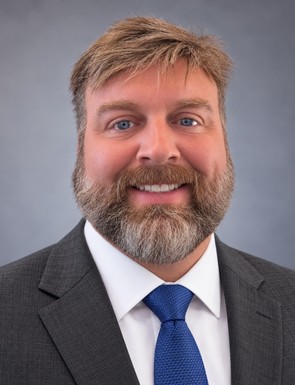
Thomas Greer, Cybersecurity Practice Director

MEET YOUR PRACTICE LEADER

Thomas Greer

Cybersecurity Practice Director

Executive cybersecurity leadership grounded in FinTech, healthcare, medical devices, compliance, risk management, and cybersecurity transformation.

From a leadership gap to an approaching audit or product milestone, start with the challenge that matters most to your organization.

LET’S FIND YOUR NEXT STEP

Turn cybersecurity into
a business advantage.

Bring your most urgent security, AI governance, or readiness challenge.
Let’s discuss where focused expertise can make a difference.

Schedule a consultation