Key takeaways
- Banning AI pushes it out of sight; an approved tool and clear rules work better.
- A simple green, yellow and red data rule tells people what can go into which tools.
- Back the policy with single sign-on, monitoring and vendor contract reviews.
Your employees are already using AI. Some use tools the company pays for; many use free accounts on personal logins, pasting in customer emails, contracts and spreadsheets to get work done faster. That unmanaged use, often called "shadow AI," is the most common AI risk in a growing company, and a short, practical AI use policy is the first fix.
Why banning AI does not work
Blanket bans push AI use out of sight rather than stopping it. People who find a tool that saves them an hour a day will keep using it. A better approach gives people a safe, approved way to use AI and clear rules about what data can go where.
What the policy should cover
- Purpose and scope. Who the policy applies to (employees, contractors) and what counts as AI, including AI features inside tools you already use.
- Approved tools. A short list of AI tools the company has reviewed and licensed, ideally business versions with single sign-on and contract terms that keep your data out of model training.
- Data rules. A simple traffic light works well:
- Green: public information can be used with any approved tool.
- Yellow: internal business information only in approved tools.
- Red: customer data, personal information, health information, credentials and confidential contracts never go into AI tools unless that specific tool has been approved for that data.
- Human review. People remain responsible for anything they produce with AI. Check facts, numbers and citations, and never let AI alone make decisions about people.
- Disclosure. When customers or others need to be told AI was used, for example in customer-facing content or automated responses.
- New AI tools and features. How to request a new tool, and who reviews it for security, privacy and contract terms.
- Training. A short session when the policy launches and as part of yearly security awareness training.
- Reporting concerns. How to report a mistake, such as sensitive data pasted into the wrong tool, without fear of punishment.
- Ownership and review. Who owns the policy and how often it is updated. AI tools change fast, so plan on at least twice a year.
Back the policy up with controls
- Turn on single sign-on for approved AI tools so access ends when someone leaves.
- Use your existing web filtering or security tools to see which AI services are in use, and block the riskiest ones.
- Apply data loss prevention rules to stop obviously sensitive data, such as health or payment information, from leaving through AI tools.
- Review AI vendors' contracts for data retention, training use and where data is stored.
How to get people to follow it
Keep the policy to about two pages, and pair it with a one-page cheat sheet. Make the approved path easier than the unapproved one. Most importantly, publish the approved tools list at the same time as the rules, so people have somewhere safe to go.
How it fits your other compliance work
An AI use policy supports SOC 2 and HIPAA programs and is one of the first documents ISO 42001 expects. If you handle health information, treat AI tools like any other vendor: no protected health information goes into a tool without a business associate agreement and a security review.
How Sollucio can help
Sollucio writes AI use policies that fit how your team actually works, reviews the AI tools you want to approve, and sets up the controls that back the policy up. We are vendor-neutral, so our recommendations are based on your needs, not on what we resell.
Next step
Not sure what your team is putting into AI tools?
We will help you find out and put sensible rules in place quickly.
About the author
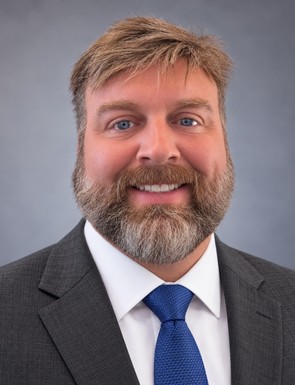
Tom Greer, CISSP, leads Sollucio’s cybersecurity practice and serves as a vCISO for growing and regulated companies. He has delivered SOC 2 and HIPAA programs for multiple organizations and built security programs from the ground up, from policy and gap assessments to roadmaps that teams can actually follow.
Related reading
Keep reading
 Private AIPrivate AI: how to use AI on your company's own knowledge without giving your data awayHow private AI lets your team use company knowledge safely, what to look for in a platform, and how Sollucio Cortex answers with sources and permissions.
 AI governanceISO 42001 explained: what an AI management system certification involves and who needs itWhat ISO/IEC 42001 requires, how it differs from ISO 27001, who needs AI management system certification and how the certification process works.Our servicesCybersecurity and AI governanceSee how Sollucio helps companies govern AI alongside security and compliance.