Key takeaways
- SOC 2 is an audit report, not a certification. Type II is what most enterprise buyers want.
- From a standing start, plan on roughly 6 to 12 months to a first Type II report.
- A tight scope and controls that run on schedule matter more than tools.
For a growing software or services company, SOC 2 usually shows up the same way: a large prospect sends a security review and asks for your SOC 2 report. If you don't have one, the deal slows down or stalls. The good news is that SOC 2 is very achievable for a small company. The bad news is that most teams underestimate how much of it is about consistent habits, not tools.
What SOC 2 is (and isn't)
SOC 2 is an audit report, issued by an independent CPA firm, that describes your security controls and says whether they meet the AICPA's Trust Services Criteria. Security is always in scope. Availability, confidentiality, processing integrity and privacy are optional, and you should add them only if your customers ask.
There is no SOC 2 "certification" and no pass/fail score. The report is what your customers read, and it says exactly where the auditor found exceptions. That is why getting ready properly matters.
There are two kinds of report:
- Type I looks at whether your controls are designed properly on a single date. It is faster and is often enough to unblock a first deal.
- Type II looks at whether your controls actually operated over a period of time, usually 3 to 12 months. This is what most enterprise customers ultimately want.
The steps
- Set the scope. Decide which product, systems, people and locations are in. A tight scope is the single biggest lever on cost and effort. Leave out systems that never touch customer data.
- Run a gap assessment. Compare how you work today against the criteria and list what is missing. Most small companies already do half of what is needed; they just don't write it down or do it on a schedule.
- Write the policies. Information security, access control, change management, incident response, vendor management, risk assessment and a few others. Keep them short and true to how you actually work. An auditor tests you against your own policies, so a policy you don't follow is worse than no policy.
- Put the controls in place. The usual list: multi-factor authentication everywhere, managed and encrypted laptops, background checks, security awareness training, onboarding and offboarding checklists, quarterly access reviews, logging and alerting, backups, vulnerability scanning and a formal process for code and infrastructure changes.
- Collect evidence as you go. Screenshots, tickets, reports and sign-offs that prove each control ran. A compliance platform can automate much of this, but it does not replace someone who owns the program.
- Pick an auditor and do the Type I. Choose a CPA firm that audits companies your size. Many companies do a readiness review with the auditor before the formal audit.
- Start the Type II window. Keep every control running and keep collecting evidence for the observation period, then the auditor tests a sample and issues the report.
A realistic timeline
For a company of 10 to 100 people with a cloud-based product, a typical path looks like this: two to four months to get ready, a Type I shortly after, then a Type II observation window of three to six months for the first report. From a standing start, plan on roughly six to twelve months to a first Type II report. Companies that already have good habits can move faster; companies with sprawling scope or no IT ownership take longer.
What trips teams up
- Scope creep. Including every system "to be safe" multiplies the evidence you have to produce, every month.
- Controls that run once. Access reviews, risk assessments and vendor reviews have to happen on the schedule your policy promises, not once before the audit.
- Offboarding gaps. A former employee or contractor who still has an active account is one of the most common audit exceptions.
- Contractors and vendors. Contractors with access to customer data are usually in scope for training, background checks and device rules. Vendors that hold your data need a review and, ideally, their own SOC 2 report.
- No single owner. When SOC 2 is everyone's side project, evidence goes missing during busy months. Someone needs to own the calendar.
- Buying a tool and stopping there. Compliance platforms are useful for tracking and evidence, but they can't decide your scope, write policies that fit how you work, or run your access reviews for you.
Where to start this month
If a customer is waiting on a report, start with the scope and the gap assessment. Those two steps tell you how far away you are and let you give the customer an honest date. Then turn on multi-factor authentication everywhere and make sure every laptop is managed and encrypted. Those controls take days, not months, and they reduce real risk right away.
How Sollucio can help
Sollucio has taken companies through SOC 2 from the first gap assessment to a clean report. We set a tight scope, write policies that match how you work, and run the program alongside your team so the controls keep operating after the audit. We are vendor-neutral, so we will work with whatever compliance tools you already use, or help you decide whether you need one at all.
Next step
Does a customer need your SOC 2 report?
We will tell you how far away you are and what a realistic timeline looks like.
About the author
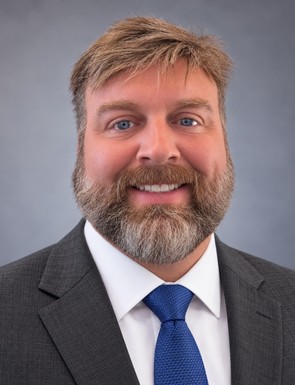
Tom Greer, CISSP, leads Sollucio’s cybersecurity practice and serves as a vCISO for growing and regulated companies. He has delivered SOC 2 and HIPAA programs for multiple organizations and built security programs from the ground up, from policy and gap assessments to roadmaps that teams can actually follow.
Related reading
Keep reading
 CybersecurityWhat a vCISO does, and when a growing company needs oneWhat a virtual CISO does, the signs your company needs one, what to look for when hiring, and what the first 90 days should cover.
 Healthcare & HIPAAHIPAA security for health-tech startups: what the Security Rule actually asks forWhat the HIPAA Security Rule requires, whether it applies to you, where startups go wrong, and a practical starting point.Our servicesCybersecurity servicesSee how Sollucio helps companies like yours, and what an engagement looks like.