Key takeaways
- Outdated or unused plugins and themes cause most website compromises.
- Named admin accounts with MFA, HTTPS with security headers, and tested off-site backups close the biggest gaps.
- About an hour a month keeps a small business site healthy.
For most small businesses, the website is the most exposed system they own. It is public, it runs software that needs regular updates, and it is often managed by whoever built it years ago. Attackers scan the internet constantly for sites with known weaknesses, and a compromised site can be used to spread malware, steal form submissions or damage your reputation with customers and search engines. Here are five checks you can run or ask your web provider about.
1. Is everything up to date, and is anything unused?
Most website compromises start with outdated software: the content management system itself, its plugins or its theme. Check that all of them are on current versions and that updates are applied at least monthly. Then remove anything you don't use. Every inactive plugin is still code an attacker can reach. When we reviewed our own website recently, removing unused plugins and applying pending updates were the first and most valuable steps.
2. Who can log in, and how?
List every account with administrator access and remove the ones that are no longer needed. Each person should have their own named account, not a shared "admin" login. Turn on multi-factor authentication for every administrator, use strong unique passwords, and limit repeated failed login attempts. If a former employee or agency still has access, close it today.
3. Is the connection secure, and does the site send security headers?
Your site should load only over HTTPS, with a valid certificate and automatic redirection from HTTP. Beyond that, a set of browser security headers tells visitors' browsers to block common attacks such as clickjacking and content injection. Free tools like securityheaders.com grade your site in seconds. Most hosting control panels or security plugins can add the headers without a developer.
4. Could you recover if the site were wiped tomorrow?
Backups should run automatically, be stored somewhere other than the web server itself, and be kept for at least a few weeks so you can roll back to a version from before a problem started. Most importantly, test a restore at least once. A backup nobody has ever restored is a hope, not a plan.
5. Would you know if something went wrong?
Use a web application firewall, either from your host or a security plugin, to block common attacks and alert you to suspicious activity. Turn on notifications for new administrator accounts and file changes, and set up Google Search Console, which will warn you if Google detects malware or hacked content on your site. Check those alerts monthly at a minimum.
A simple monthly routine
Once the five checks are in place, keeping the site healthy takes about an hour a month: apply updates, confirm backups ran, review administrator accounts, and look over security alerts. Put it on someone's calendar and it will actually happen.
When to get help
If your site was built by someone who is no longer around, runs software nobody updates, or collects customer information through forms, it is worth a professional review. The same goes for any business that has to answer security questionnaires from customers, since your website is often the first thing a reviewer looks at.
How Sollucio can help
Sollucio's cybersecurity practice reviews and hardens business websites as part of a broader security program, from updates and access controls to monitoring and backup testing. We also track active threats to common website software and publish advisories, such as our PHP2Shell advisory.
Next step
Want a second opinion on your website?
We will walk through these five checks with you.
About the author
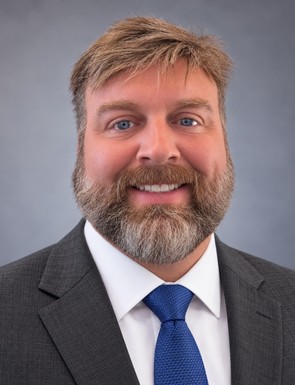
Tom Greer, CISSP, leads Sollucio’s cybersecurity practice and serves as a vCISO for growing and regulated companies. He has delivered SOC 2 and HIPAA programs for multiple organizations and built security programs from the ground up, from policy and gap assessments to roadmaps that teams can actually follow.
Related reading
Keep reading
 CybersecurityWhat a vCISO does, and when a growing company needs oneWhat a virtual CISO does, the signs your company needs one, what to look for when hiring, and what the first 90 days should cover.
 ComplianceSOC 2 readiness for a small company: the steps, the timeline, and what trips teams upThe steps to SOC 2 for a small company, a realistic timeline from gap assessment to Type II report, and the mistakes that cause audit exceptions.Our servicesCybersecurity servicesSee how Sollucio helps companies like yours, and what an engagement looks like.